
cybersecurity
Security nightmare for US as National Security Agency network suddenly goes dark

The disruption has been serious enough to affect how personnel report for work at the agency’s headquarters at Fort Meade. Photo credit: Samuel Boivin/Shutterstock
The agency responsible for protecting America’s national security has been hit by a major technical failure, after its highly classified internal communications network went down, leaving officials scrambling to establish the extent of the disruption. The system is used to exchange sensitive intelligence, raising serious questions about how the country’s most secretive security organisation is managing without reliable access to its own communications infrastructure.
The National Security Agency (NSA), one of America’s most powerful intelligence organisations, is investigating problems affecting its internal network, known as NSA Net. The system allows employees to communicate classified information within the agency. Its disruption was first reported by CNN on Tuesday, November 17, citing six people familiar with the situation. There is currently no evidence that the incident was caused by a cyberattack, but the agency has yet to establish publicly the full extent of the problem.
Staff told to stagger their arrivals
The disruption has been serious enough to affect how personnel report for work at the agency’s headquarters at Fort Meade, Maryland. According to sources speaking to CNN, the NSA introduced staggered arrival times while it investigated the problem. Further details emerged through cybersecurity publication The Record, which reported that the network had been experiencing intermittent service rather than being completely shut down.
One source told the publication that officials were trying to avoid tens of thousands of employees attempting to sign into the system simultaneously, putting additional pressure on an already unstable network. Another source said NSA Net had been unreliable for weeks, causing frustration among staff before the latest disruption became public. The agency has not confirmed the technical cause or explained when normal service is expected to resume.
What happens when America’s intelligence network fails?
The problem is particularly concerning because the NSA plays a central role in gathering and analysing foreign signals intelligence, including communications and electronic signals. Its work also includes helping protect US government communications and information systems.
A disruption to the network used by its own personnel to exchange classified information is therefore more than an ordinary office IT problem. Reliable communications are essential when intelligence needs to be shared securely between teams working on national security matters. However, there is an important distinction between the failure of NSA Net and the agency losing its ability to carry out its entire mission.
The United States has backup facilities and alternative secure communications systems. According to current and former US officials quoted by CNN, these redundancies mean urgent intelligence can still be communicated securely to President Donald Trump while he is travelling in Asia. The Record also reported that backup NSA centres around the country were expected to help maintain the agency’s intelligence-gathering operations during the disruption.
No evidence of a cyberattack
With a highly classified intelligence network involved, the possibility of hostile interference is an obvious concern. However, investigators have not identified evidence that hackers were responsible. Reuters independently reported CNN’s findings on Tuesday, confirming that the NSA was working to establish the scope of the problem.
The agency had not immediately responded to requests for comment. The cause remains unknown, and it would be premature to describe the incident as a security breach or an attack by a foreign government.
Another major cyber incident raises eyebrows
The NSA outage comes after a major Microsoft 365 disruption on November 13, which left users in several countries struggling to access Outlook and other workplace services. Problems affected Exchange Online, with some users unable to open mailboxes, send emails or access parts of Microsoft Teams. Microsoft attributed the disruption to problems affecting its infrastructure and said there was no indication it had been caused by a cyberattack.
It also comes amid reports of a separate cyberattack involving websites belonging to major organisations, including the BBC and IKEA. The attack exploited a vulnerability in the third-party Optimizely platform, with malicious code injected into affected customer websites.
Whether either incident is connected to the NSA outage remains unknown. There is currently no evidence linking the website attack or the Microsoft service disruption to the problems affecting the agency’s classified network. For now, the biggest unanswered questions remain what caused NSA Net to become unstable, how extensively the disruption has affected personnel and when reliable service will be restored. The NSA has not publicly explained the cause or provided a timetable for resolving the problem.



One of the most disruptive problems involved Apple Account and iCloud sign-ins. Photo credit: Lester Balajadia/Shutterstock
Apple users have been left unable to access some of the services they rely on to use their iPhones, make payments and manage their digital lives, after problems hit several parts of the company’s online systems on Tuesday, November 17. Reports of trouble surged across services including iCloud, the App Store, Apple Pay and Apple Support, with some customers saying they had been unexpectedly signed out of their accounts and then could not get back in.
Others reported that apps would not download, music services were failing to connect or devices could not complete activation. For anyone relying on iCloud to reach photos, files or contacts, or trying to pay for something through Apple Pay, even a temporary loss of access can quickly become more than an inconvenience.
Users locked out of Apple accounts
One of the most disruptive problems involved Apple Account and iCloud sign-ins. Users reported being logged out on iPhones and Macs, only to encounter verification failures or error messages when they tried to sign in again. The problems also appeared to affect the App Store, where customers reported difficulties loading the service and downloading applications. Apple Music, iPhone activation and App Store Connect, the platform used by developers to manage their apps, were among the other services mentioned in outage reports.
Apple Pay and Apple Support also featured in reports from users experiencing difficulties. However, the precise impact varied, and the volume of complaints does not mean every customer or every Apple service was affected.
What Apple has confirmed
Apple’s own System Status page briefly acknowledged problems with Apple Account sign-in, warning that the service might be slow or unavailable. The company also reported an issue with Subscription Purchase, which could have affected customers trying to complete subscription transactions. That subscription issue was marked as resolved after around three hours. The wider wave of user reports, however, extended beyond the services Apple had formally listed.
Technology publication 9to5Mac reported that Downdetector was showing a sharp rise in complaints across several Apple services, even while Apple’s general status page continued to show some of them as available. The publication also noted reports from developers struggling to access App Store Connect. The discrepancy left customers trying to establish whether a problem was with their own device or an Apple service. There has been no public explanation from Apple identifying one cause for all the reported problems, nor has the company confirmed that every service named in user complaints suffered an outage.
How widespread was the disruption?
Reports were not confined to one product or one type of customer. Problems were flagged across account access, cloud storage, app downloads, digital payments and developer services. That range made the disruption particularly frustrating for people using several parts of Apple’s ecosystem together. However, outage-monitoring websites such as Downdetector rely on reports submitted by users. A spike can indicate that many people are experiencing difficulties, but it does not independently establish how many customers were affected or prove that a service was completely unavailable.
The problems come amid a series of high-profile technology disruptions affecting major companies and essential services. Microsoft 365 suffered a widespread outage on November 13,, rather than malicious activity. The same day as Apple’s disruption, the National Security Agency’s highly classified internal communications network, NSA Net, also experienced problems. The recent problems have also included a technical failure that prompted a nationwide flight ground stop in the United States and disruption to banking services.
Apple’s official System Status page remains the best place to check its own updates: Apple System Status. The cause of Tuesday’s problems remains unclear. Apple has not announced a single explanation for the wider reports, and there is no evidence that the disruption was caused by a cyberattack. For customers suddenly locked out of accounts or unable to use services they normally take for granted, the wait for a clear explanation may be almost as frustrating as the outage itself.
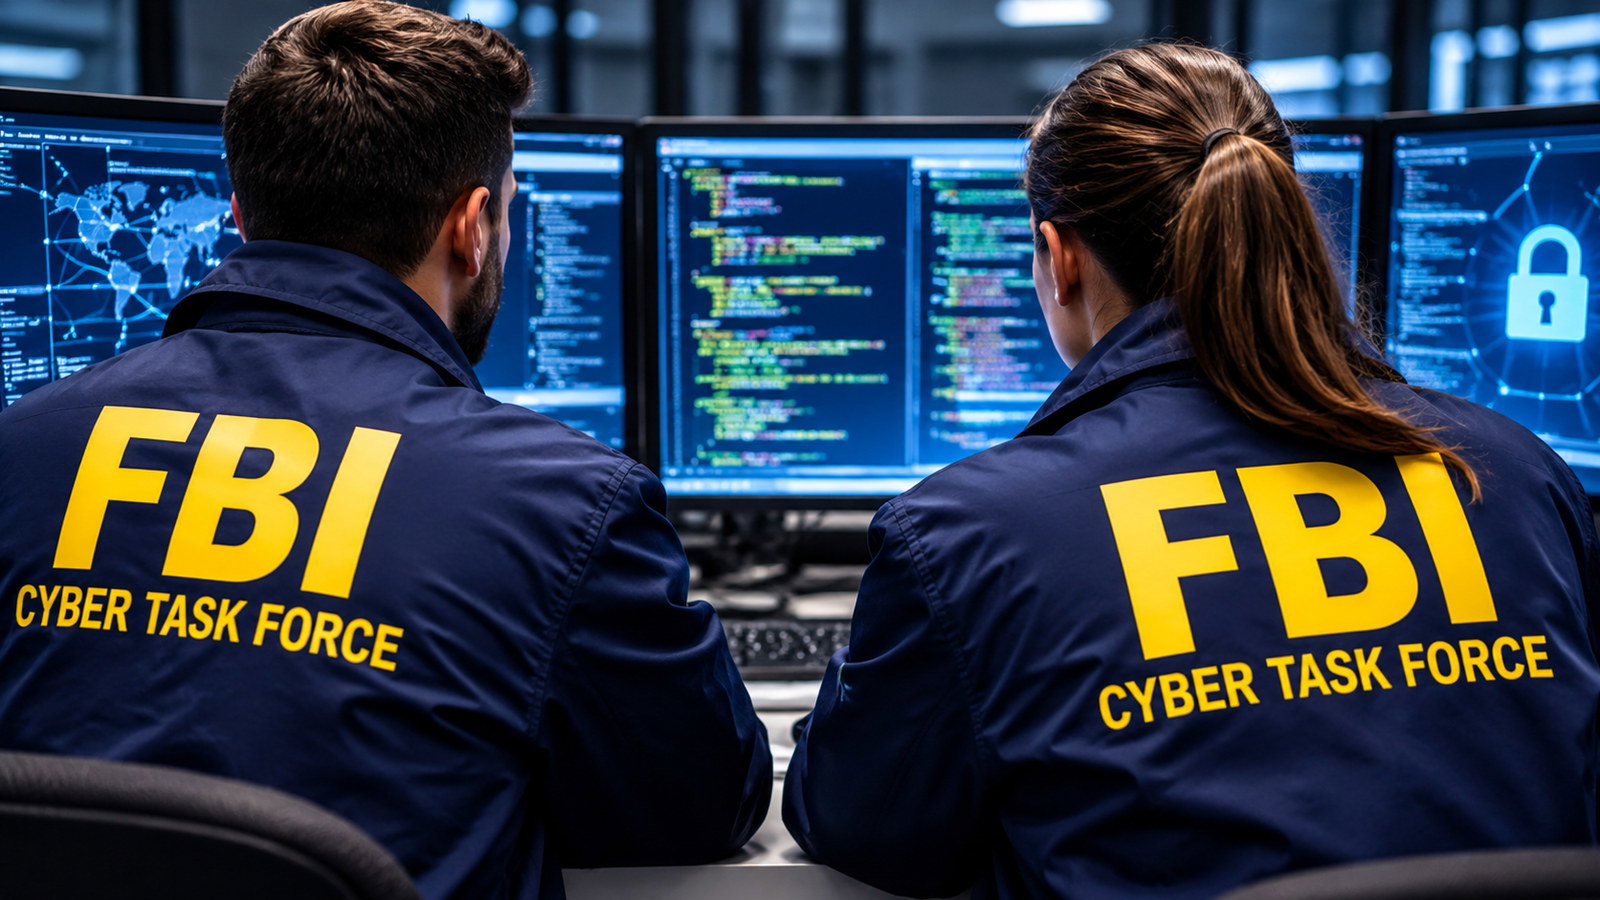
FBI cyber investigators as the agency warns of threats to essential services across Europe. Credit: AI generated illustration.
American investigators warn of growing cyber threats to essential services as bomb alerts reach British broadcasters and Spain’s Foreign Minister raises concerns about psychological warfare across Europe.
Passengers have faced flight diversions, television staff have been evacuated and businesses across Europe are being warned that hackers could interfere with equipment protecting food and medical supplies. Now the FBI has issued an international cybersecurity warning, while Spain’s Foreign Minister, José Manuel Albares, has suggested that the wave of disruption could be part of a wider campaign of hybrid aggression and psychological warfare. With Britain’s Sky among the broadcasters receiving threats on Friday, November 6, the concerns extend well beyond airports and computer networks.
FBI warns hackers could disrupt essential services
In an official warning issued on November 5, FBI Cyber Division chief Brett Leatherman urged businesses to strengthen security around industrial refrigeration and temperature monitoring systems used to protect food, medicine and other essential supplies. Investigators highlighted outdated equipment, exposed internet connections and unchanged factory passwords as weaknesses that could allow attackers to manipulate temperatures remotely, potentially destroying valuable stock and disrupting vital services.
The warning follows attacks already affecting European businesses and medical facilities, including the incident involving three French blood service sites previously covered in Euro Weekly News’ investigation into the blood bank cyberattack. Rather than focusing on that incident again, the FBI’s latest message is about prevention, urging organisations to restrict remote access, update vulnerable equipment and ensure temperature alarms can alert staff before serious damage occurs.
Bomb threats spread to British and European broadcasters
The cybersecurity warning comes as European authorities investigate a separate wave of bomb threats that has disrupted passenger flights and reached television stations. On Friday, Ireland’s RTÉ, Britain’s Sky and Bulgaria’s Nova TV received threats, prompting evacuations and security investigations. According to Reuters, RTÉ temporarily suspended normal programming, while the alerts followed several days of aviation disruption involving flight diversions and emergency security checks. No explosives were discovered in the reported incidents, and investigators have not established who was responsible.
Spain’s Foreign Minister raises fears of psychological warfare
Spain’s Foreign Minister José Manuel Albares has raised the possibility that the bomb threats are part of something more deliberate. Speaking to Spanish broadcaster RTVE on November 6, he described the aviation alerts as a possible form of hybrid aggression and psychological warfare, suggesting that spreading fear and disrupting everyday life could be among the objectives. His remarks, reported by Reuters, come as European authorities investigate whether the incidents share a common origin.
The developments add urgency to concerns previously examined in Euro Weekly News’ report on hybrid warfare and security threats across Europe. However, the FBI has not established any connection between the refrigeration attacks and the bomb alerts, and investigators have not identified a government or organisation responsible for the wider incidents.
For people living in Britain, Spain and elsewhere in Europe, the immediate concern is how quickly everyday services can be disrupted, whether through hackers exploiting vulnerable technology or security threats that force authorities to take precautionary action. The FBI’s warning is a reminder that protecting essential infrastructure is no longer just a concern for governments and major corporations, but also for the businesses and services millions of people depend on every day.

Spain’s railway chaos deepens as minimum services ignored and fresh strike threatens
Dogs on the loose: Two AP-7 incidents raise Costa del Sol safety concerns
Costa del Jive brings swinging fun back to Benalmadena


-
 New Developments2 weeks ago
Luxury Villas For Sale, Estepona – ProjectL1
-
Age Concern Marbella - San Pedro3 weeks ago
Halloween lunch sells out as 51 join Marbella get-together
-
 New Developments3 weeks ago
How To Get A Tourist Rental Licence In Andalusia (Spain) – Step-By-Step Guide 2025
-
 %3 weeks ago
Spain Orders Replacement Of Eight Million Gas Meters: New Rules, Costs And Deadlines
-
 New Developments2 weeks ago
The San Roque Club – Townhouses For Sale
-
Barcelona riots3 weeks ago
Looting and street violence hit Barcelona as El Corte Inglés customers are trapped
-
countryside2 weeks ago
Rural revival: Five Almeria villages make moving inland easier and more enticing
-
 New Developments4 weeks ago
Inside The Most LUXURIOUS Apartment Building In Spain!